Analyzing A Reverse Shell
Analysis of a reverse-shell RAT sample, tracing how it calls back to its operator and what it can do on an infected host.
In this post, I am going to analyze another RAT downloaded from the HuskyHacks GitHub page.
This is the information I have on the file before analyzing.
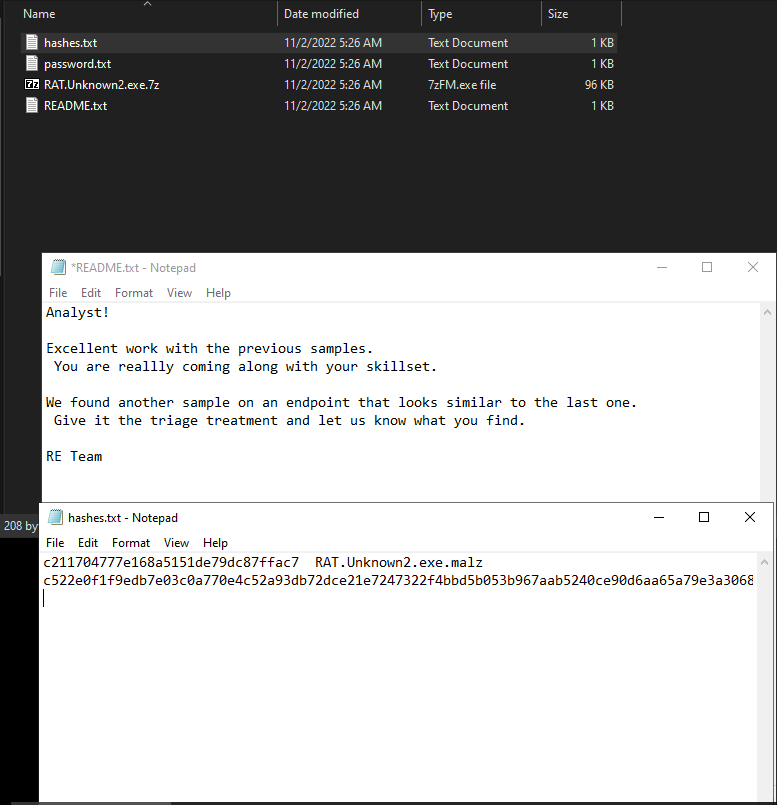
I have a message from the IR team telling me they found another sample that looks similar to the last one, and there is also a txt file with hashes.
I extracted strings using FLOSS but didn't find anything valuable.
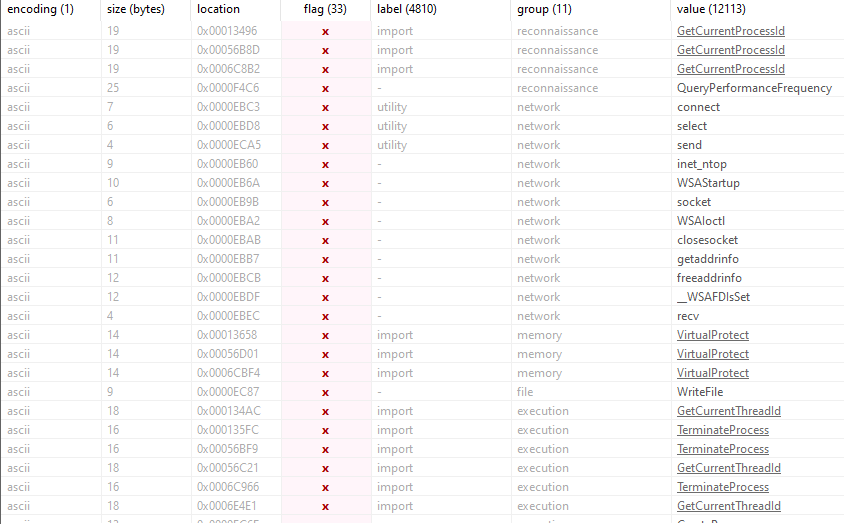
After looking again with PEstudio it looks like there might be a socket capability.
Moving on to dynamic analysis.
Initial Detonation.
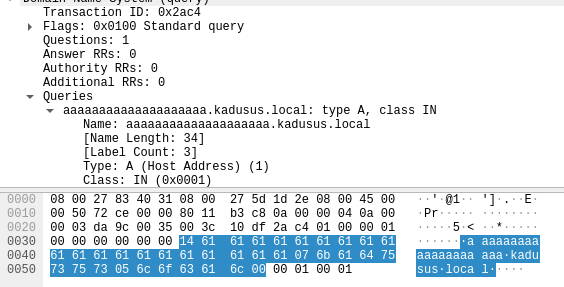
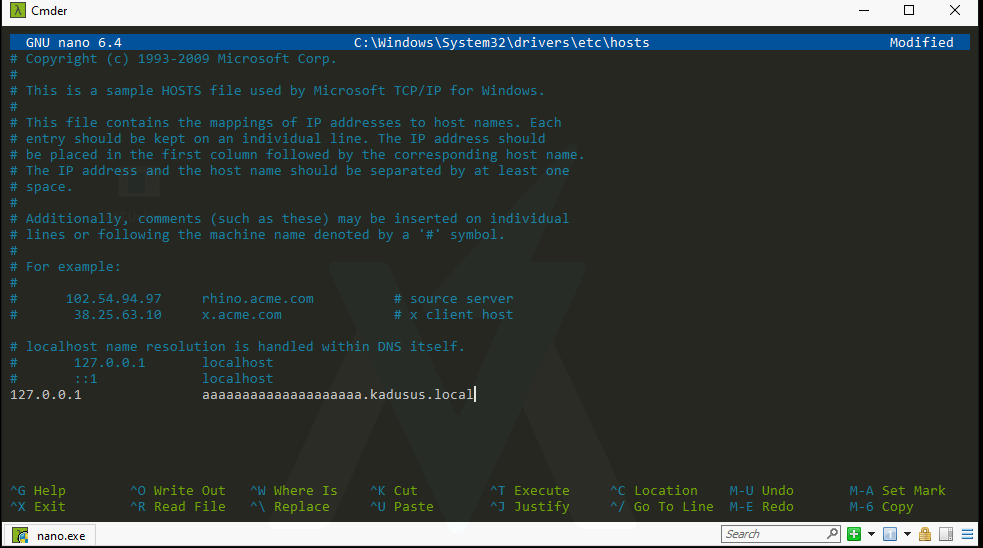
A record DNS: aaa...kadusus.local
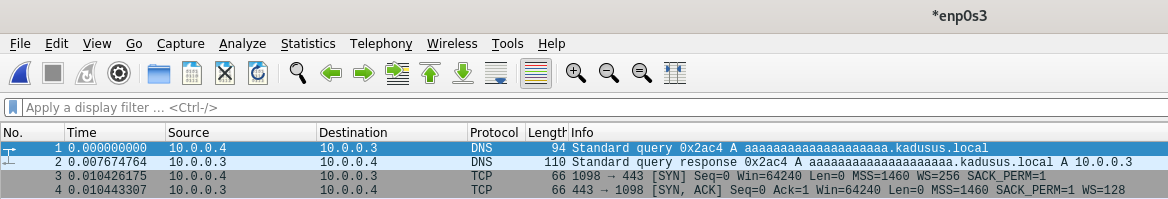
Adding the address to the hosts file
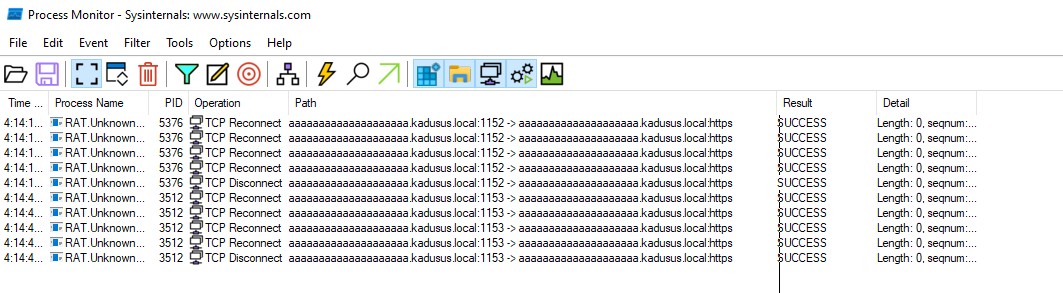
Potential call out to specified DNS record on HTTPS port (443)
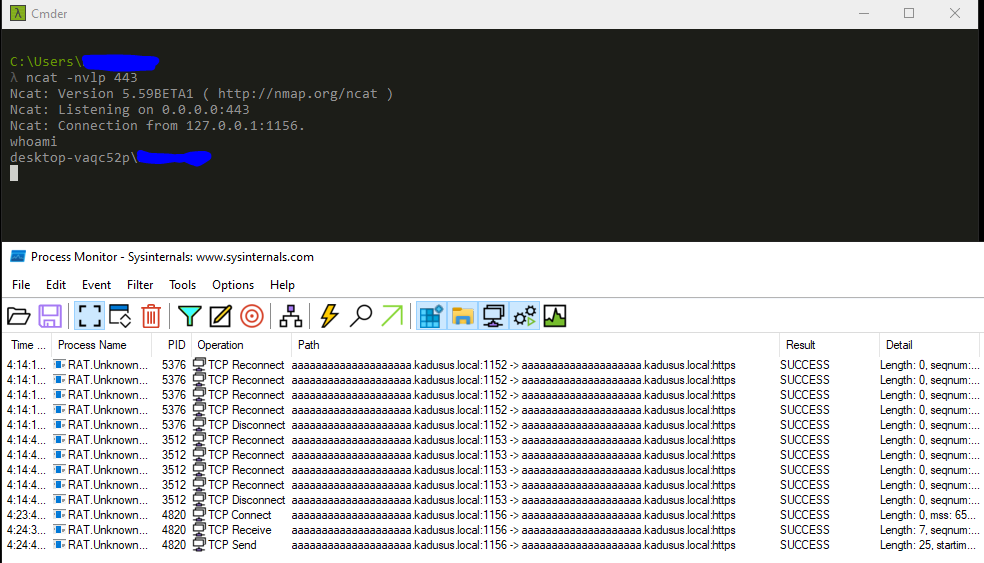
Reverse shell capabilities
Conclusion:
Seems like the file has reverse shell capabilities and I managed to run some commands to verify my conclusions.
Thank you for reading and I hope you found this post interesting.